Introduction
AI labs want training data they are allowed to use, and they want proof to go with it. On October 12, 2026, DATA Network said it will move its protocol onto Sui and use Walrus as its default storage, according to Sui. Its registry, Trace, had logged more than 286 million receipts for contributed files by October 25, 2026, per its own live counter.
The pitch is AI training data provenance that regulators and legal teams will accept. A Trace receipt shows that a file with a given fingerprint was registered by a given app, under stated terms, before a given time. It does not show that the uploader owned the file, that everyone in it agreed, or that the license would hold up in court.
This article covers how a receipt is made, what Walrus stores, what the record can and cannot prove, and where courts and regulators stand.
What DATA Network Is After the Story Rebrand
DATA Network is not a new project. It is Story Protocol, which spent 2025 building a blockchain for licensing intellectual property. On June 25, 2026, CEO Andrea Muttoni wrote that “Story is becoming The DATA Foundation, $IP becomes $DATA, Story Network becomes DATA Network,” in a foundation post.
The same post explains the turn. Broad IP licensing proved harder than expected, because “companies behind the most valuable music, games, and brands guard their most valuable IPs jealously.” The demand came from AI training data instead. Story first saw it through Poseidon, a data project it had incubated. Poseidon cleans, checks and scores contributed data, and it screens out content that is scraped, synthetic or altered.
What Changed With the Move to Sui
The October announcement goes further. DATA Network will stop running its own chain and become a protocol on Sui. Walrus becomes the default storage layer for the foundation’s apps, and the Sui Foundation said it is putting $30 million into the network, per Sui’s blog. Tokens carry over one-to-one. The old chain keeps running until the upgrade is done, and no date has been set.
Crypto.news noted that the size of the stake, the deal terms and whether the full sum has moved were not disclosed. It also noted that Trace’s figures come from the foundation and have not been audited by anyone outside it.
The Pieces in the Stack
| Piece | What it does | Status as of October 25, 2026 |
| Trace | Public registry of receipts for contributed files | Live since June 2026 |
| Poseidon | Cleans, checks and scores datasets | Running on DATA, per the foundation |
| Sui | Base chain for the protocol | Move announced, no date |
| Walrus | Storage, plus an encrypted copy of each file | Announced, copies described as a future feature |
| Confidential Data Rails | Rules for using encrypted data without exposing it | Slated for Q3 2026 in the June post, no launch confirmed as of October 21 |
| TEEs for evals and fine tuning | Sealed hardware runs that can be checked | Described as a future possibility |
How a Trace Receipt Gets Made
Trace does not store anyone’s files. It stores receipts. Trace’s site describes four steps.
- A contributing app, such as Kled or Numo, collects a file with the user’s consent and keeps sensitive details in its own systems.
- The app sends Trace a receipt for that one file through a signed webhook. The receipt is anchored by the file’s SHA-256 hash, a fingerprint that changes if a single byte of the file changes.
- Trace groups receipts into batches and writes one Merkle root per batch onchain. A Merkle root works like a fingerprint for the whole batch, so changing any receipt inside it breaks the match.
- Anyone can look up a receipt. A lab can upload a list of hashes and see the consent, terms, KYC and file type coverage for a whole dataset.
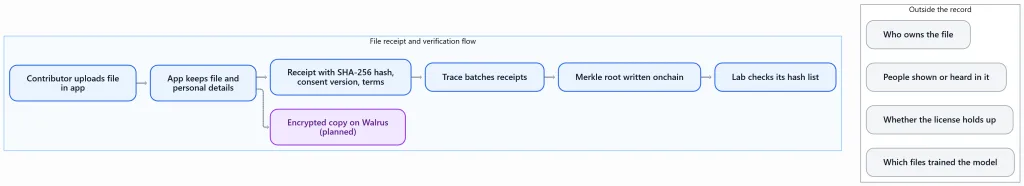
The foundation says each record shows a content hash, signed consent, versioned license terms, payment status, compliance details and a log of contribution, usage and payment events. Contributor identities are anonymized, and the data itself stays confidential, per the June post.
One detail matters more than the rest.
The receipt is a statement made by the app. Trace checks the app’s signature, fingerprints the receipt and timestamps it. Trace never sees the file, so it cannot check the file against what the app says about it.
What Walrus Stores, and Who Can Read It
The October plan adds a second layer. Walrus will hold an encrypted copy of each contributed file, one that cannot be changed, as a reference point. Because a Trace hash can be rebuilt from the data itself, a lab could later check a processed file against the original, per Sui. This is described as future work.
Walrus is public by default. Its documentation says it plainly. “All blobs uploaded to Walrus are publicly available,” per the Walrus docs. Each file gets an ID derived from its content. Sui holds the certificates and metadata, while storage nodes hold the pieces of the file. A file is guaranteed to stay available until the end of the storage period someone paid for, and it can be marked deletable.
So the promise that data is “only readable by licensed buyers,” in Sui’s words, rests on encryption. Sui’s own docs pair Walrus with Seal for that job, though the October announcement does not say which tool DATA will use.
Seal encrypts a file so that a group of key servers releases decryption keys only when an onchain rule written in Move approves the request, per the Sui docs. A threshold, such as three of five servers, stops any single operator from opening the file alone. Removing a licensee from an allowlist stops new keys. The docs say nothing about copies a licensee already decrypted, and they warn that upgrading the policy package can rewrite who gets access.
That is the normal limit of access control. It decides who can open the file next. It cannot pull back a copy that has already left.
What an Onchain Record Proves
Start with the problem Trace was built for. The Data Provenance Initiative audited more than 1,800 text datasets and found licenses missing more than 70% of the time on popular hosting sites, and miscategorized more than 50% of the time, per its published audit. Labs often cannot say where their data came from or under what terms.
Against that baseline, a receipt adds real information. An explainer from exchange Bitrue sums it up as “a Trace record proves that a file was registered and when.” That is accurate, and a little more can be said.
| A Trace receipt can show | Why it holds |
| A file with this exact hash was registered by this app | The hash is unique to the file, and the app signs the receipt |
| It was registered before a known time | The batch root is written onchain with a timestamp |
| The receipt has not been changed since | Any change breaks the batch root, and updates are chained in a log |
| Which consent version and terms the app says applied | These fields travel with the receipt |
| Whether a lab’s dataset matches registered files | A lab can check its own hashes against Trace |
| Whether processed data matches the original | Possible once Walrus copies exist |
These are useful facts. They make it hard to invent a consent record after the fact, or to swap a file once it has been registered. A lab facing a dispute could show that its files matched receipts written months earlier.
What It Cannot Prove
Every row above is a fact about the record. Rights are facts about the world, and the record cannot reach most of them.
Who Owns the File
A receipt shows which app sent it and, through its KYC fields, whether the uploader’s identity was checked. Identity is not ownership. A verified person can still upload a photo someone else took, a song playing in the background or a page from a book. Trace cannot tell, because it never sees the file.
Everyone Who Appears in It
Kled, the largest source of receipts, runs 108 task templates that use the camera, microphone, screen recording, touch and keyboard, per Solana Compass. A street video or a screen recording can capture people who never opened the app. The receipt records the uploader’s consent version. It holds nothing about anyone else in the frame.
Consent That Survives GDPR
Under EU law, “The data subject shall have the right to withdraw his or her consent at any time,” per Article 7(3) of the GDPR. That right sits awkwardly next to a record designed never to change.
The EDPB, the board of EU privacy regulators, adopted its final guidelines on blockchains on July 7, 2026. They say “it is not advisable to store personal data on the blockchain,” and they warn that “all encryption systems have an undetermined, but limited, lifespan,” per the EDPB guidelines. A summary of the guidelines adds that hashes linked to other identifiers can still count as personal data. It also says consent should not be the legal basis when a system cannot delete a person’s data.
Trace keeps personal details with the app and puts hashes onchain, which follows the EDPB’s direction. The planned Walrus copies are harder to square. An unchangeable encrypted copy of a person’s voice or face is the kind of record the guidelines say will not stay sealed forever. Neither DATA nor Sui has said how a withdrawal request would be handled once those copies exist.
A License That Holds Up
A receipt carries the terms an app set. Whether those terms cover a given use, and whether the uploader had the power to grant them, is a question for contracts and courts. The receipt is evidence in that fight. It does not decide it.
What a Model Actually Learned From
Receipts describe input files. They say nothing about which files went into a training run, or whether a lab mixed registered data with scraped data. Closing that gap needs a record of the run itself.
Muttoni pointed in that direction, with “potentially fully verifiable TEEs for evals and fine tunings in the future,” per Sui. A TEE is a sealed area of a chip that can prove what code ran inside it, a design explained in NEAR Protocol: What It Is and Why AI Needs It. For now, it is a plan.
Whether the File Is Real
Paying per upload invites fake uploads, a pattern covered in Sybil Attacks in Decentralized AI Networks: What Works. DATA relies on Poseidon to screen out scraped, synthetic and altered content. Kled says its own fraud model removes 98.4% of bad actors within their first 10 uploads, but it has not published the tests behind that figure, per Solana Compass. A receipt confirms that a file was registered. It does not grade it.
Where the Law Draws the Line
Courts and regulators are starting to say what training data needs. None of them asks for an onchain receipt, but two recent cases show why a paper trail matters. This section describes rules and rulings for context. It is not legal advice.
The EU AI Act
Providers of general-purpose AI models released from August 2, 2025, have had to keep a copyright policy and publish a summary of their training content. Models already on the market before that date have until August 2, 2027. The European Commission gained the power to enforce those rules on August 2, 2026, with fines of up to 3% of global turnover or €15 million, whichever is higher, per the AI Act Explorer.
The Commission’s template asks providers to say whether they used licensed content, to list the top 10% of domains they scraped, and to explain how they respected opt-outs, per WilmerHale. It does not ask for proof of each license. Trace can help a lab fill in the licensed-content part of that summary. It does not make the lab compliant by itself.
Thomson Reuters v. Ross
On September 29, 2026, the Third Circuit ruled that training a legal research tool on Westlaw’s headnotes was not fair use. Baker Botts calls it what appears to be the first federal appeals ruling on whether AI training is fair use. The court found that “the evidence shows that the market for licensing headnotes as text to train AI is rapidly developing.” It limited the ruling to AI that does not generate new expression.
For DATA, the ruling cuts both ways. A market for training licenses that a court recognizes makes licensed data worth more. It also makes training without a license riskier.
Bartz v. Anthropic
Judge William Alsup ruled that Anthropic could train on books it had bought. Jurist reports his finding that “Anthropic had no entitlement to use pirated copies for a central library.” The case settled for $1.5 billion, covering more than 400,000 books at $3,000 each, and won final approval on July 20, 2026.
This is the clearest case so far of provenance carrying legal weight. How the books were acquired decided which side of the line they fell on. A record of that acquisition would have mattered because of the facts it captured, not because of where it was stored.
The Numbers Behind Trace
These figures come from Trace’s live counter, read on October 25, 2026.
| Measure | Figure | Share of receipts |
| Receipts on the protocol | 286,966,561 | 100% |
| From Kled | 281,198,321 | 98.24% |
| From Numo | 5,018,519 | 1.75% |
| From oto | 13,179 | Under 0.01% |
| Contributors | 542,276 | |
| Data audited | 377.71 TB |
Two things stand out. The first is concentration. Kled sent 98.24% of all receipts, and its founder, Avi Patel, is also the DATA Foundation’s Chief Data Officer, per Crypto Briefing. That does not make the receipts wrong. It does mean Trace’s scale rests on one app, run by someone inside the foundation, whose consent flow no outside party has audited.
The second is that the counts do not line up. The June post described “over 1.1 billion records being registered on DATA chain” through Kled. A press release the next day said “Kled has begun the process of registering 1.5 billion user-contributed records,” per GlobeNewswire. Four months later, Trace shows about 281 million Kled receipts. Records on the chain and receipts on Trace may count different things. Neither DATA nor Kled has published a reconciliation.
The same lesson came up with agent registries. ERC-8004 Adoption: What the Agent Numbers Actually Show found that more than 170,000 registered agents did not add up to real adoption. A count of registrations tells you how many claims were filed, not how many hold up.
How Other Projects Handle AI Training Data Provenance
DATA is not the only project trying to prove where data came from. Each one checks a different slice of the problem.
| Project | What it checks | Where the check happens | What it leaves open |
| DATA Network (Trace) | Consent version, terms, KYC and file fingerprint, as reported by the app | App side, with batch roots onchain | Whether the app’s claims are true |
| Vana | Authenticity, ownership, quality and uniqueness, per Vana’s docs | Validators inside a TEE | The docs list no limits, and each data group writes its own check |
| Grass | Where scraped web data came from, for one of its two traffic types | Grass’s validator | Whether each site allowed scraping |
| Ocean Protocol | Lets algorithms run on data that never leaves its source | The data owner’s setup | Whether the owner had the right to share the data |
| Hedera with EQTY Lab | Signed records of model training runs, per The New Stack | Chip TEEs, logged on Hedera | The rights in the training inputs |
Further reading. Grass Revenue and the Home Internet Behind AI Training Data ends by asking what provenance record comes with each dataset. Trace is one answer to that question, with the limits set out above.
Ocean’s approach keeps data with its owner while models learn from it, covered in Ocean Protocol (OCEAN): What Its Data-Sharing Protocol Does. Read side by side, these projects split the work. Trace logs claims, Vana tests data, Grass traces web origin, and Hedera logs training runs. None of them proves a right on its own.
Real Use Cases, Sorted by Maturity
Live. Kled, Numo and oto write receipts to Trace. Anyone can look a receipt up, and a lab can check a list of hashes against the registry. A $12 million non-exclusive data licensing deal for Kled was reported in June, with no counterparty named, per Solana Compass.
Announced. The move to Sui, Walrus storage with an encrypted copy of each file, and TEEs for evals and fine tuning. None of these has a date.
Unconfirmed. Confidential Data Rails was slated for mainnet in Q3 2026, and no launch has been confirmed. Sui’s announcement says Numo and oto already license data to frontier AI labs and robotics companies, but none of those customers is named.
The Risks Behind the Receipts
One app carries the registry. Almost every receipt comes from Kled, whose founder holds a senior role at the foundation. If Kled’s consent flow has a gap, nearly the whole registry has the same gap.
The chain is changing under the receipts. Receipts are anchored on DATA’s own chain, and that chain will shut down after the move to Sui. The transition plan has not been published. A lab relying on older receipts needs them to stay checkable after the switch.
Storage is public unless encryption is set up right. Walrus files are open by default. Privacy depends on encrypting before upload, on key servers run by separate operators, and on who controls upgrades to the access policy.
Permanent copies meet deletion rights. EU regulators say encryption has a limited lifespan and advise against storing personal data onchain. An unchangeable copy of a person’s voice or face will test that advice.
The numbers are self-reported. Receipt counts, contributor counts and Kled’s fraud figures all come from the companies. No outside audit has been published.
What This Means for AI Labs, Data Contributors and Builders
AI Labs
Treat a Trace receipt as the start of due diligence, not the end. Ask each contributing app for the consent text behind every version number, the KYC provider it uses, how it handles people other than the uploader, and how it processes deletion requests. Keep your own record of which files went into each training run, since Trace does not track that.
Data Contributors
A receipt shows what you agreed to and when. Before you upload, check whether your files will be copied to Walrus and how withdrawing consent works once they are. If your footage shows other people, the same questions apply to them, and they never saw the app’s terms.
Builders
Trace’s basic pattern is sound. Keep personal data offchain, anchor fingerprints onchain, and use salted hashes, since the EDPB treats plain hashes as too weak for public chains. If you store files on Walrus, encrypt them before upload and spread Seal key servers across independent operators. Lock down who can upgrade the policy package, because an upgrade can change who gets access.
What to Watch
The first marker is the migration plan, and whether receipts written on DATA’s old chain stay verifiable on Sui. The second is a named AI lab that says it has licensed Trace-registered data.
A third would be an outside audit that samples receipts and checks them against the files and consent records behind them. Watch also for how deletion requests are handled once Walrus copies exist, and for a confirmed launch of Confidential Data Rails.
Conclusion
Trace does something labs have lacked. It turns scattered consent forms and license terms into fingerprints and timestamps that anyone can check and nobody can quietly edit later.
That is evidence, not title. AI training data provenance on a blockchain can show what an app claimed, about which file, and when. Ownership, the consent of everyone in the file and the strength of the license are settled by contracts, privacy law and courts.
So, the useful question for a lab is not whether data is onchain. It is who made the claim in the receipt, and who has checked it.
FAQs.
What is DATA Network’s Trace registry?
Trace is a public registry for AI training data run by the DATA Foundation, which was Story Protocol until a June 2026 rebrand. Contributing apps such as Kled and Numo send Trace a receipt for each file, anchored by its SHA-256 hash and carrying consent and license terms. Trace batches those receipts into Merkle roots onchain. It never stores the files, so a receipt records what an app claimed about a file, not the file itself.
Does a Trace receipt prove I own my data?
No. A receipt shows that an app registered a file with a given fingerprint, under stated terms, before a given time. KYC fields can show that the uploader’s identity was checked, but identity is not ownership. A verified person can still upload a photo someone else took or a recording of someone else’s voice. Ownership depends on who created the file and what rights they hold, and Trace never sees the file.
What happens if I withdraw consent after my file is registered?
The GDPR gives people in the EU the right to withdraw consent at any time. DATA has not published how withdrawal works for Trace receipts or for the encrypted Walrus copies it plans to keep. EU privacy regulators advise against storing personal data onchain and warn that encryption has a limited lifespan. Before you upload, check the contributing app’s terms for how it handles deletion requests and who it shares files with.
Can anyone download files registered on Trace?
No. Trace stores receipts, not files, and sensitive details stay with the contributing app. The planned Walrus copies are different. Walrus makes every stored file publicly available by default, so those copies would depend on encryption. Seal, the access tool Sui pairs with Walrus, releases keys only when an onchain rule approves. Removing a licensee stops new keys, but nothing in Seal’s docs pulls back a copy that was already decrypted.
Does Trace make an AI lab compliant with the EU AI Act?
Not on its own. The Act asks general-purpose model providers for a copyright policy and a public summary of training content, enforceable since August 2, 2026. The Commission’s template asks whether licensed content was used, not for proof of each license. Trace receipts can support that licensed-content section. The lab still has to describe its other sources, explain how it respected opt-outs and keep its own record of what each model was trained on.
Subscribe below for no-hype AI crypto analysis before the market catches up.
Editorial & Disclaimer Note: Content on CryptoAIAnalysis is independently researched and written using publicly available documentation, technical resources, and observable network data. The aim is to explain AI-powered crypto and blockchain systems clearly, highlight real-world use cases, and discuss limitations alongside potential. This content is provided for informational and educational purposes only and does not constitute financial, investment, or legal advice. Cryptocurrency and AI-related investments involve risk, and readers should always conduct their own research before making decisions.